Continuity, cyber recovery, compliance, and sovereignty each grew their own stack with a backup array here, a DR site there, GRC tooling bolted on, and copies scattered across jurisdictions. The seams between them are where resilience fails.
Operational Resilience
Keep Running, Recover Clean, and Stay in Control
Attacks, outages, audits, and residency mandates are operating conditions now, not edge cases you plan for once a year. Resilience cannot be a slow tier you fall back to after the damage is done. VAST builds continuity, recovery, governance, and sovereignty into the primary platform. It's a property of the system, not a stack bolted around it.
The Resilience Gap
Four Kinds of Disruption, Four Separate Silos to Survive Them
Recovery Measured in Days
Restoring petabytes from disk or tape runs sequentially, so a fully encrypted estate turns a bad day into a multi-week outage while revenue and trust drain away.
Backups and Controls You Cannot Trust
Attackers hit the backups first, and audit trails stitched together after the fact can't prove what happened. If your recovery copy or your evidence can be altered, neither one counts.
Continuity and Sovereignty That Cost Twice
A warm DR site idles at full cost, and meeting data-residency rules usually means yet another copy in yet another region, paying repeatedly for capacity that mostly waits.
VAST allows us to seamlessly bring benefits to clients, ensuring that their critical data assets are safeguarded from malicious attacks, like ransomware, and they can recover very quickly to minimize disruptions.
Preben Berg
CTO, Advania Managed Services

Why Now
Resilience Can No Longer Live Outside the System
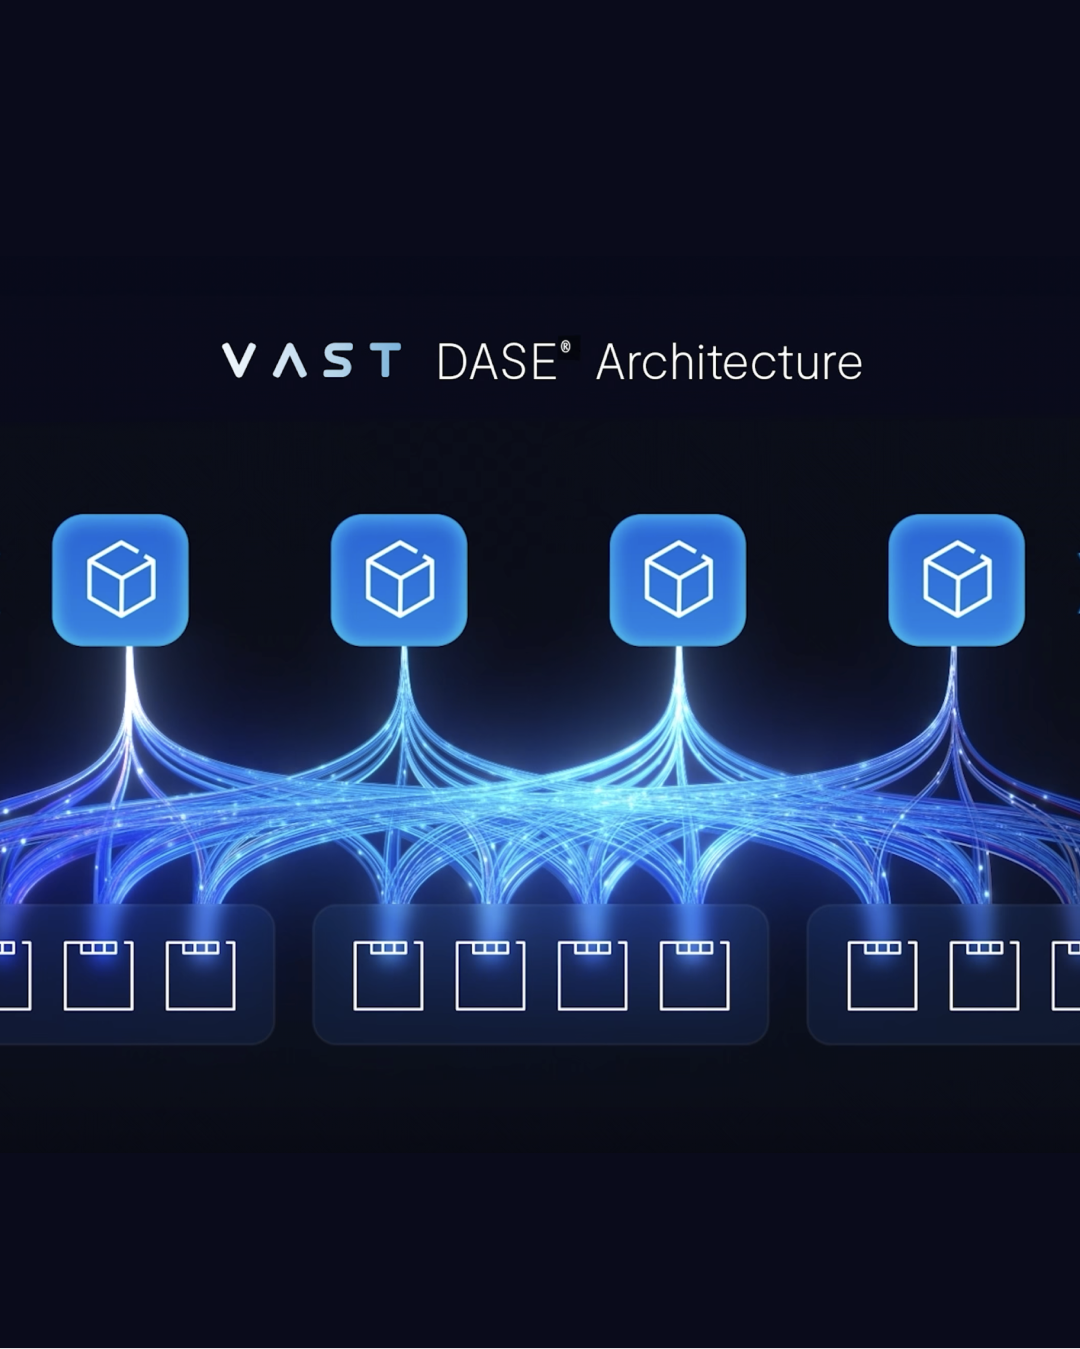
For decades, resilience was something you added around your data. Protection meant copying it to a separate estate; continuity meant a second site that idled until disaster; compliance meant GRC tools reconstructing what happened after the fact; and sovereignty meant yet another copy pinned to a region. Each layer was a separate purchase, a separate seam, and a separate point of failure. Two shifts ended that model. Attacks now target the recovery copy and the audit trail directly, and regulators, from data-residency laws to operational-resilience mandates, expect continuous proof of control, not once a year. Bolt-on resilience cannot keep that pace. VAST's Disaggregated Shared-Everything (DASE) architecture changes the equation by making protection, availability, governance, and locality intrinsic properties of the primary tier. Immutable snapshots, wide erasure coding, a global namespace, and native access control and audit live in the platform itself, so the copy attackers cannot reach, the site that takes over, the audit trail, and the jurisdiction boundary are all the same system, not four you integrate. For the first time, the system you run production on is the same system that recovers it, proves it, and keeps it under your own control and jurisdiction, one operational-resilience foundation instead of four.
The VAST AI Operating System
One Foundation for Continuity, Recovery, Governance, and Sovereignty
VAST DataStore and VAST DataSpace make resilience an intrinsic property of the platform. Immutable snapshots defend against attack, flash-native recovery collapses restore times, one global namespace keeps data available across sites, and governance and locality are enforced in place, not reconstructed by tools bolted around the data.
Recover at Flash Speed
Restore from immutable snapshots that read at the same speed as production. Recovery becomes minutes, not the days it takes to rehydrate petabytes from disk or tape.
Protect Data That Cannot Be Altered
Immutable snapshots mean the copy an attacker cannot reach is the one you recover from. Backups stop being the soft target that gets encrypted first.
Stay Available Through Failure
DASE tolerates SSD, node, and site loss without stopping work. Non-disruptive upgrades and replication keep production running through the events that used to force an outage.
Prove Control and Keep Data in Jurisdiction
Access control, immutability, retention, and a single audit trail are properties of the namespace, and one namespace spans your sites and sovereign clouds, so compliance and residency are enforced in place, not bolted on.
How VAST Delivers Operational Resilience
Availability, Recovery, and Control is Built Into the Architecture
Immutable Recovery Attackers Cannot Reach
Backups on a separate system are exactly what an intruder finds, alters, or deletes before springing the ransom. VAST writes immutable snapshots that cannot be changed or removed within their retention window, even with administrator credentials, and reads them back at flash speed. The clean point stays intact, and recovery is measured in minutes.
Governance and Sovereignty Enforced in the Namespace
Audit trails reconstructed after a breach are only as trustworthy as the system that was breached, and residency rules usually mean scattered copies. VAST makes access control, immutability, and retention native to the namespace and answers who touched what and when against one governed copy, and lets that namespace span your own sites and sovereign clouds, so proof of control is continuous, and data (with the AI that operates on it) stays inside the jurisdiction that governs it.
Why VAST DataStore?
The Primary Tier That Recovers and Protects Itself
VAST DataStore persists files, objects, and volumes as native Elements in one all-flash namespace on the DASE architecture. That same architecture makes it the resilience tier: wide erasure coding, immutable snapshots, and flash-speed reads mean the storage you run production on is the storage you recover from. No separate backup array, no cold tier, no rehydration.
Indestructible Immutable Snapshots
Snapshots cannot be altered or deleted within their retention window, even with administrator credentials. The clean point stays intact when the primary system is compromised, giving you a trusted place to restore from.
11 Nines Durability at Exabyte Scale
Wide erasure stripes tolerate four simultaneous SSD failures at 2.7% overhead, delivering 11 nines of durability. Data survives hardware loss without a rebuild storm degrading the systems still running.
Non-Disruptive by Design
Stateless CNodes and shared NVMe storage let you upgrade, patch, and expand without downtime. Maintenance stops being a scheduled outage, and the events that once forced a failover no longer do.
Why VAST DataSpace?
One Namespace Across Every Site, Cloud, and Jurisdiction
VAST DataSpace turns the primary namespace into a distributed one, extending the same data across on-premises sites, cloud regions, sovereign clouds, and edge locations with synchronous and asynchronous replication and Global Clones, so continuity and sovereignty do not require a duplicate estate that idles until it is needed.
Replicate Without Rebuilding
Synchronous and asynchronous replication keep a remote copy current within one namespace. A synchronous target holds an identical copy at commit time; an asynchronous one trails by a defined interval you set to your recovery goal.
Survive Site Loss
When a location goes dark, applications reach the same data from another site or cloud. Continuity becomes reroute-to-the-namespace rather than rebuild-from-backup.
Keep Data in Its Jurisdiction
Pin data and the AI that operates on it to the regions and sovereign clouds your mandates require, without copy sprawl or egress fees, sovereignty enforced by the namespace itself.
Resilience Across Industries
Where Downtime, Data Loss, and Non-Compliance Are Not Options
The cost of a slow recovery, an outage, a failed audit, or a residency breach reads differently in every industry, but the requirement is the same: keep running, recover clean, and prove control. See how VAST delivers operational resilience where the stakes are highest.